Gmail is Google's email service for consumer and Google Workspace accounts.
It can be connected to Agen.co two ways, matching the Official / In-house filter in the connector picker:
- Official — Agen.co connects through Google's own hosted Gmail MCP server, so your AI agents use the same message, thread, draft, and label tools Google exposes to MCP clients like Claude and Antigravity.
- In-house — Agen.co wraps the Gmail API directly through its own integration layer, using a dedicated OAuth client you register in Google Cloud Console.
Pick Official if the built-in MCP tools cover what your agents need. Fall back to In-house if you need broader API coverage — for example, managing forwarding rules, aliases, or per-user settings.
Prerequisites
Prerequisites
- A Google account with access to Google Cloud Console
- A Google Cloud project with the Gmail API and Gmail MCP API enabled
- In Google Cloud Console, select your project and enable the Gmail API and the Gmail MCP API.
- Go to APIs & Services → Credentials and click Create credentials → OAuth client ID.
- Set Application type to Web application and give it a name (for example,
Agen.co Gmail MCP). - Switch back to Agen.co, go to Connectors → My connectors, click Add connector, and in the search bar type
Gmailand select it from the results. - Get back to Google Cloud Console. Under Authorized redirect URIs, click Add URI and add both URLs Agen.co generates when you open the Add Gmail panel with Official selected:
- Callback URL — completes the initial OAuth handshake between Agen.co and your OAuth client.
- Gateway callback URL — used by the Agen.co MCP gateway for per-user authorization at runtime.
- Click Create, then copy the Client ID and Client Secret — the Client Secret is shown only once.
Keep your Client Secret safe
Keep your Client Secret safe
The Client Secret is shown only once. If you lose it, return to the client's detail page and generate a new one.
- In the left sidebar, go to APIs & Services → OAuth consent screen → Data access, and add the following scopes:
| Scope | Description |
|---|---|
https://www.googleapis.com/auth/gmail.readonly | Read all messages, threads, labels, and drafts |
https://www.googleapis.com/auth/gmail.modify | Manage labels and move messages or threads to Trash or Spam |
- Return to the Agen.co portal — the Add Gmail panel should already be open from step 4. Fill in the fields:
| Field | Required | Description |
|---|---|---|
| Instance Slug | Yes | Prefixes each imported tool as slug__tool, so a second instance of the same connector needs a slug of its own. Use lowercase kebab-case. You can change it later from the connector's settings. |
| Client ID | Yes | The Client ID from the OAuth client you created above. |
| Client Secret | Yes | The Client Secret from the OAuth client you created above. |
- Click Connect.
- You're redirected to Google to sign in and approve access.
- Return to Agen.co and click Add below the list of tools that were added.
Once connected, Gmail appears under My connectors with tools spanning:
| Area | What it covers |
|---|---|
| Messages | Searching, listing, and reading messages; moving them to Trash or Spam |
| Threads | Listing and reading conversation threads |
| Drafts | Creating, listing, and reading drafts |
| Labels | Listing and managing labels |
The Official MCP server creates drafts but does not send mail. Use the In-house tab if your agents need to send messages.
Enabling the Gmail connector isn't enough on its own. Tool calls remain denied until you create a policy that grants access to the specific tools you want to expose.
Integrating Gmail with Frontegg allows your application to read, send, and manage email messages, threads, labels, and drafts in users' Gmail mailboxes — all through Frontegg's integration layer using Google OAuth 2.0.
Prerequisites
Prerequisites
- A Google account with access to Google Cloud Console
- A Google Cloud project (you can create one during setup)
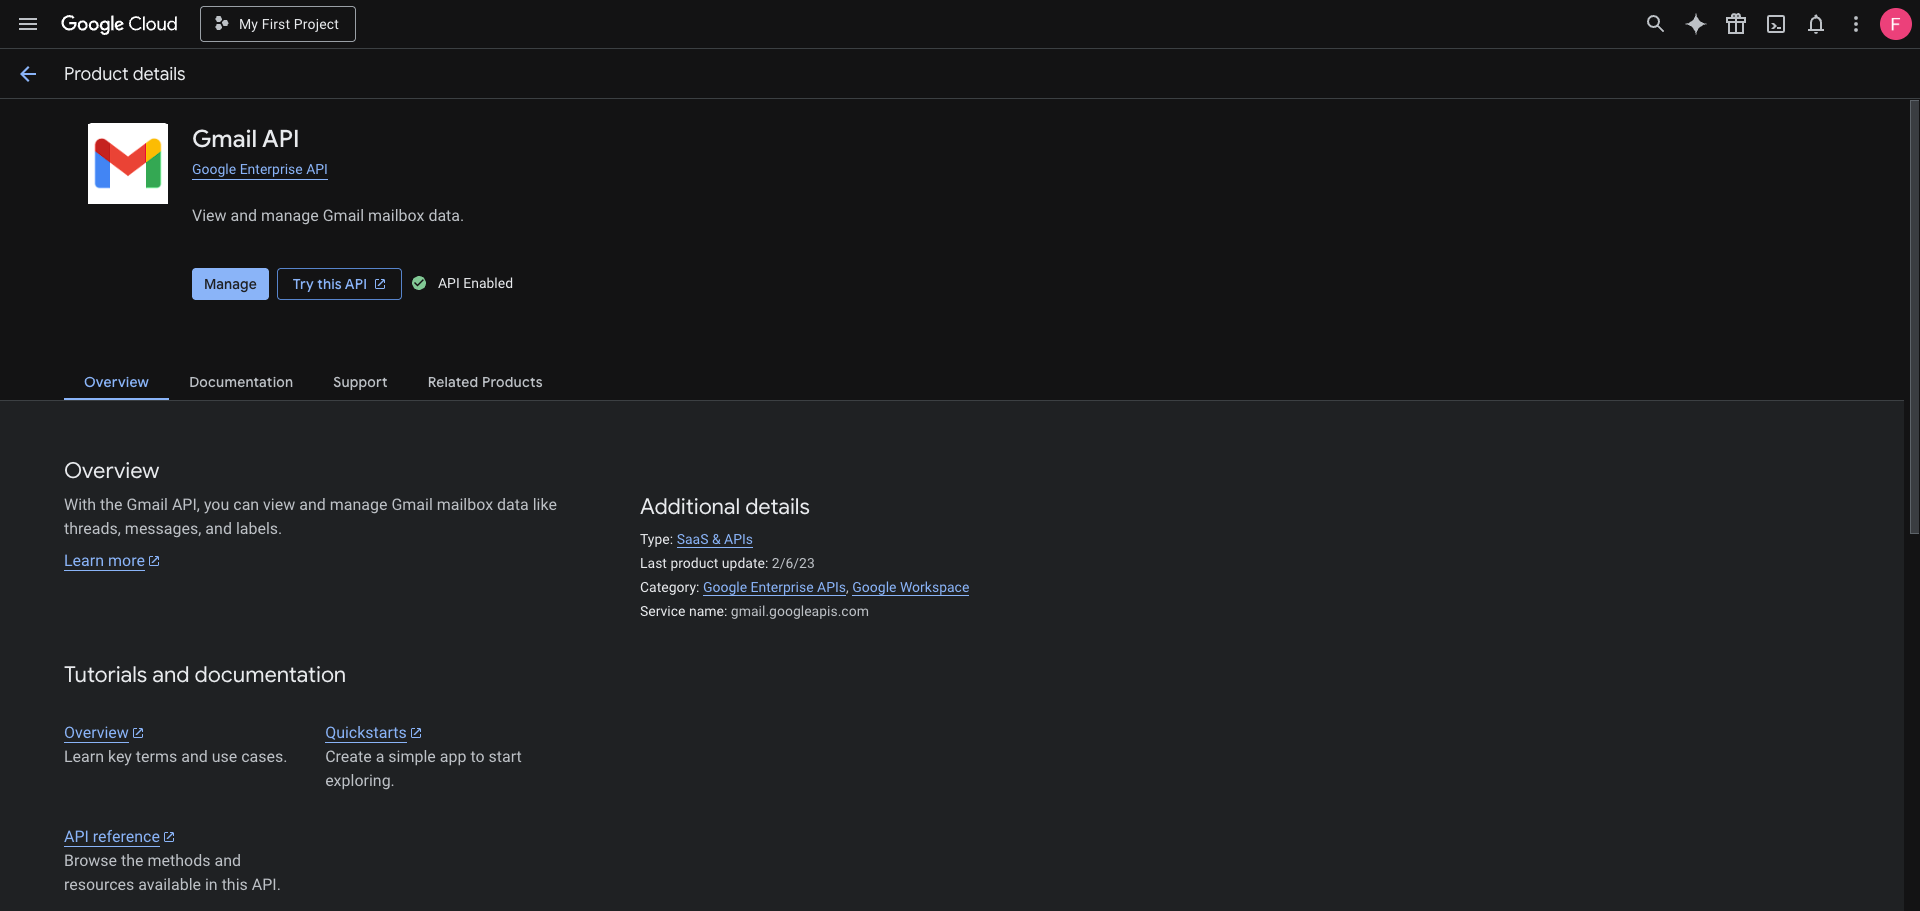
Go to the Gmail API page in the Google Cloud Console. Select your project from the top navigation, then click Enable if the API is not yet enabled. If you see Manage and API Enabled, the API is already active.
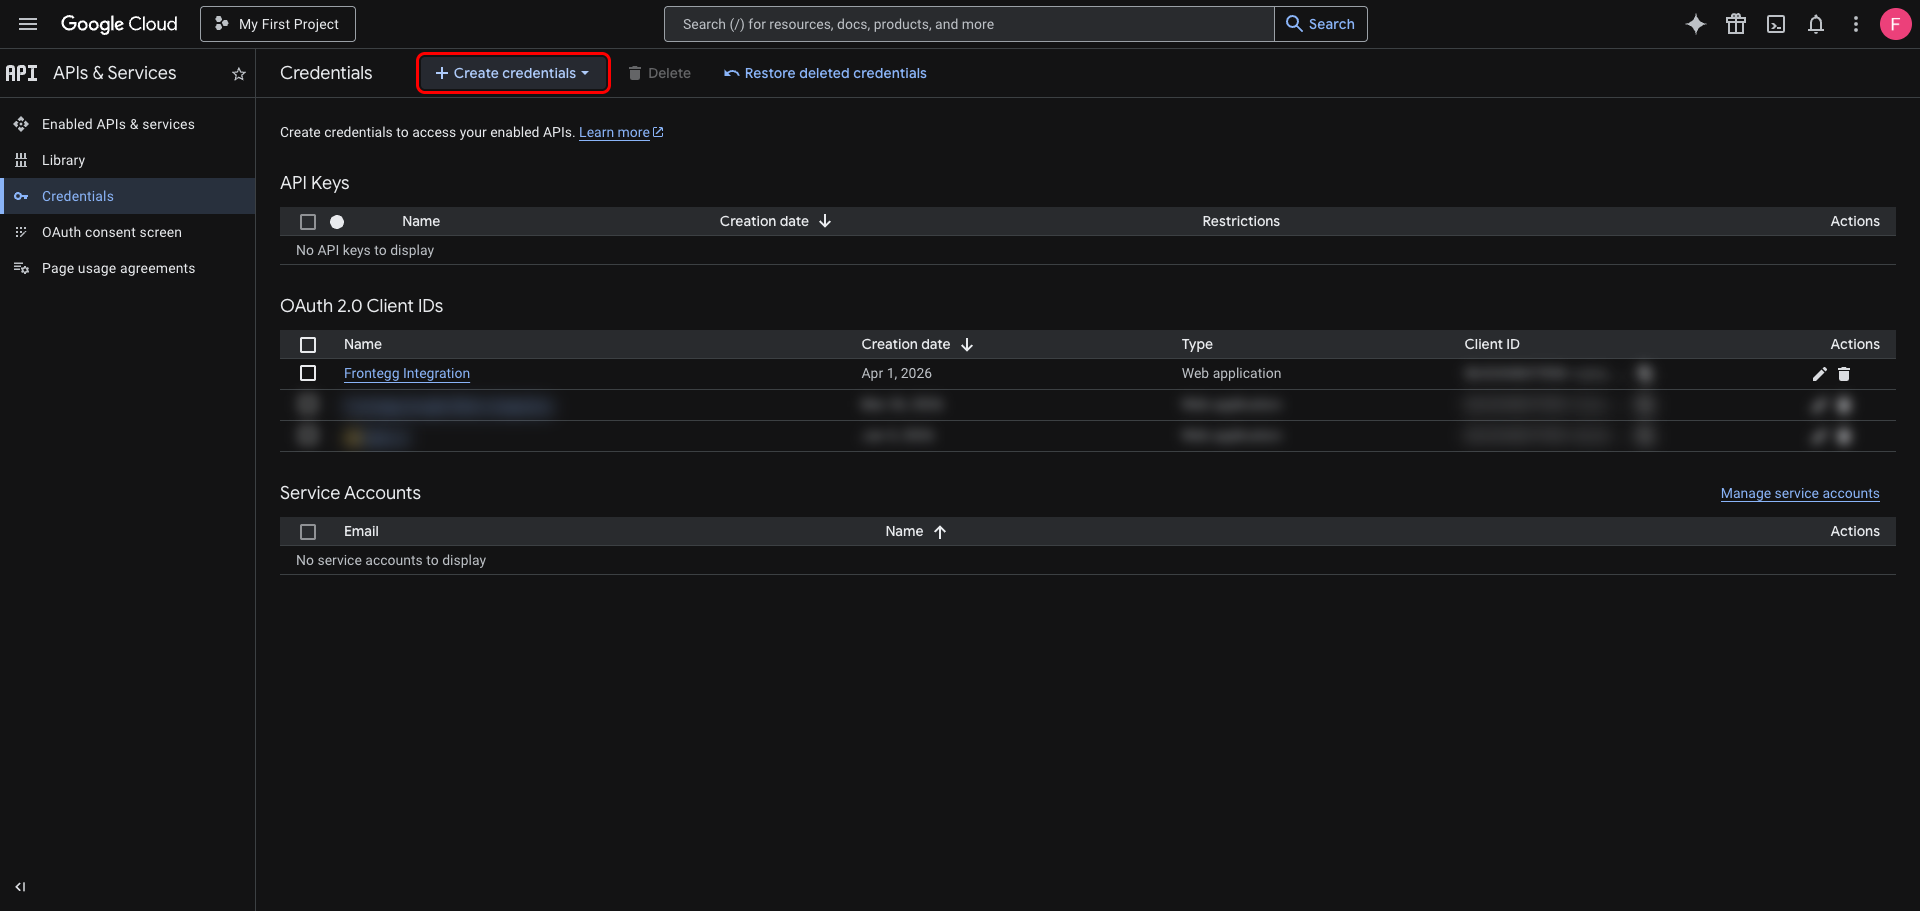
In the left sidebar, navigate to APIs & Services → Credentials. Click Create credentials.
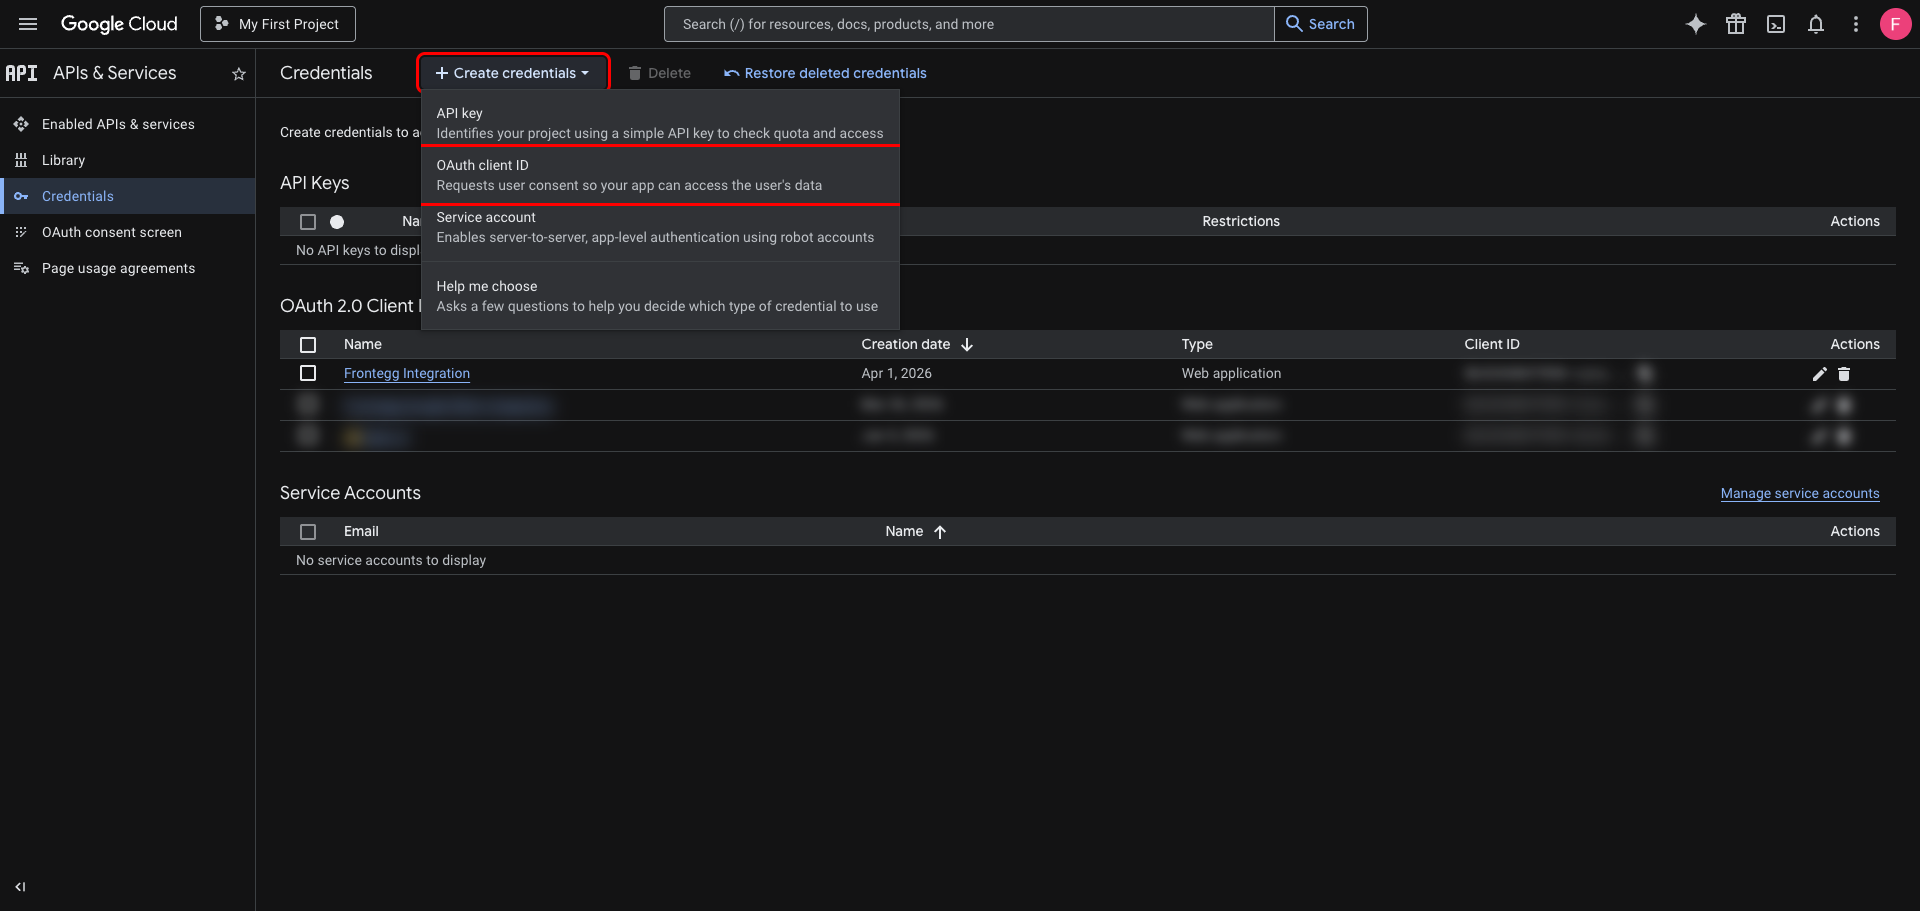
From the dropdown, select OAuth client ID.
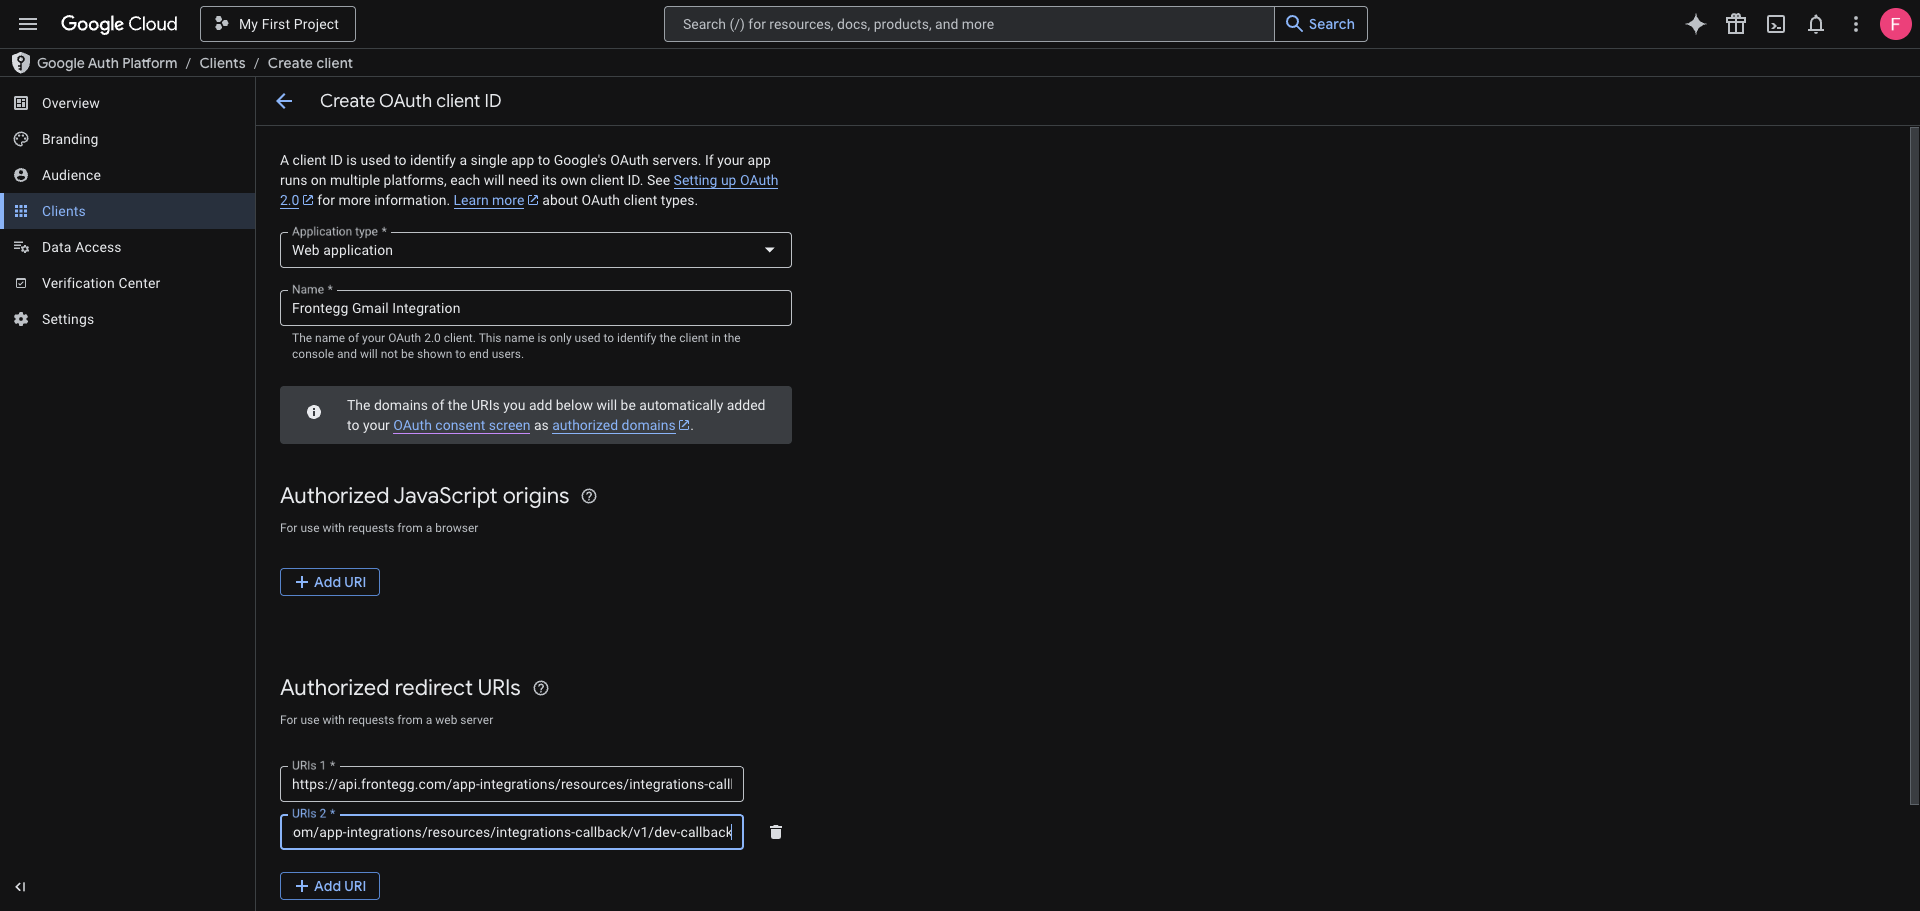
On the Create OAuth client ID page:
- Set Application type to Web application.
- Enter a name for the client (for example,
Frontegg Gmail Integration). - Under Authorized redirect URIs, click Add URI and add both of the following:
https://YOUR_MCP_GATEWAY_URL/integration-callback
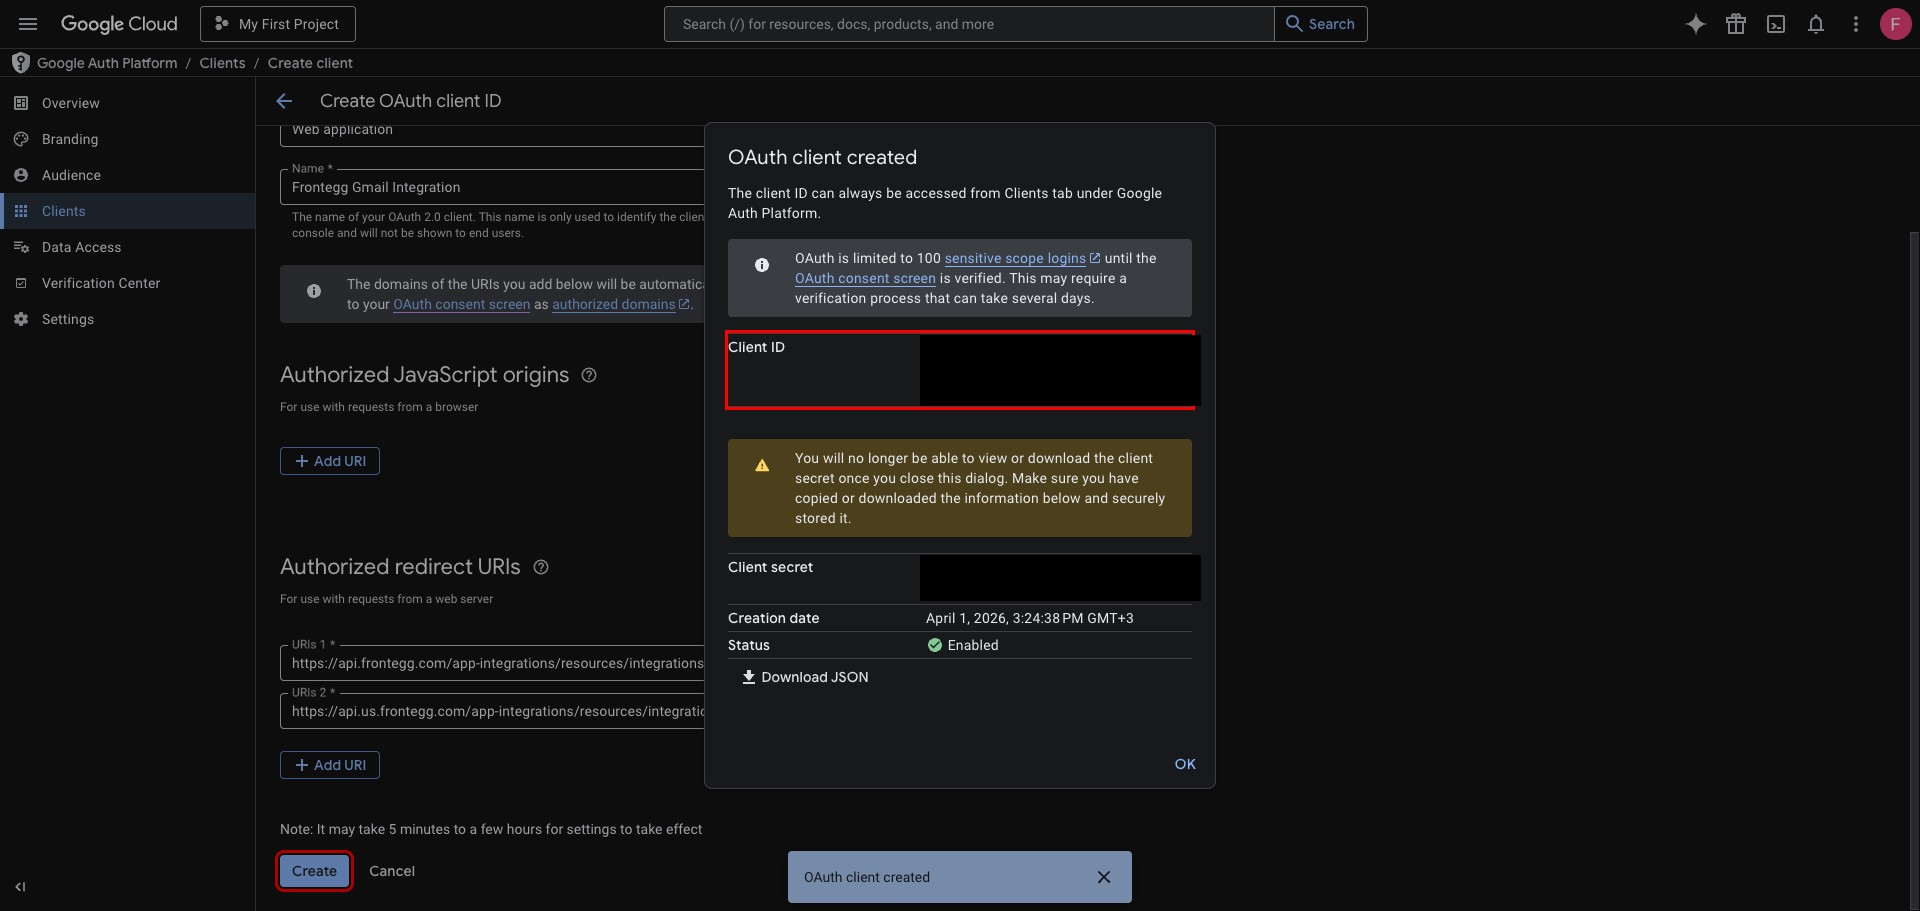
Click Create to save the OAuth client. A dialog will display your Client ID and Client Secret — copy both values and store them securely.
Save your Client Secret now
Save your Client Secret now
The Client Secret is only shown once in this dialog. After you close it, you cannot retrieve it again — you can only create a new secret.
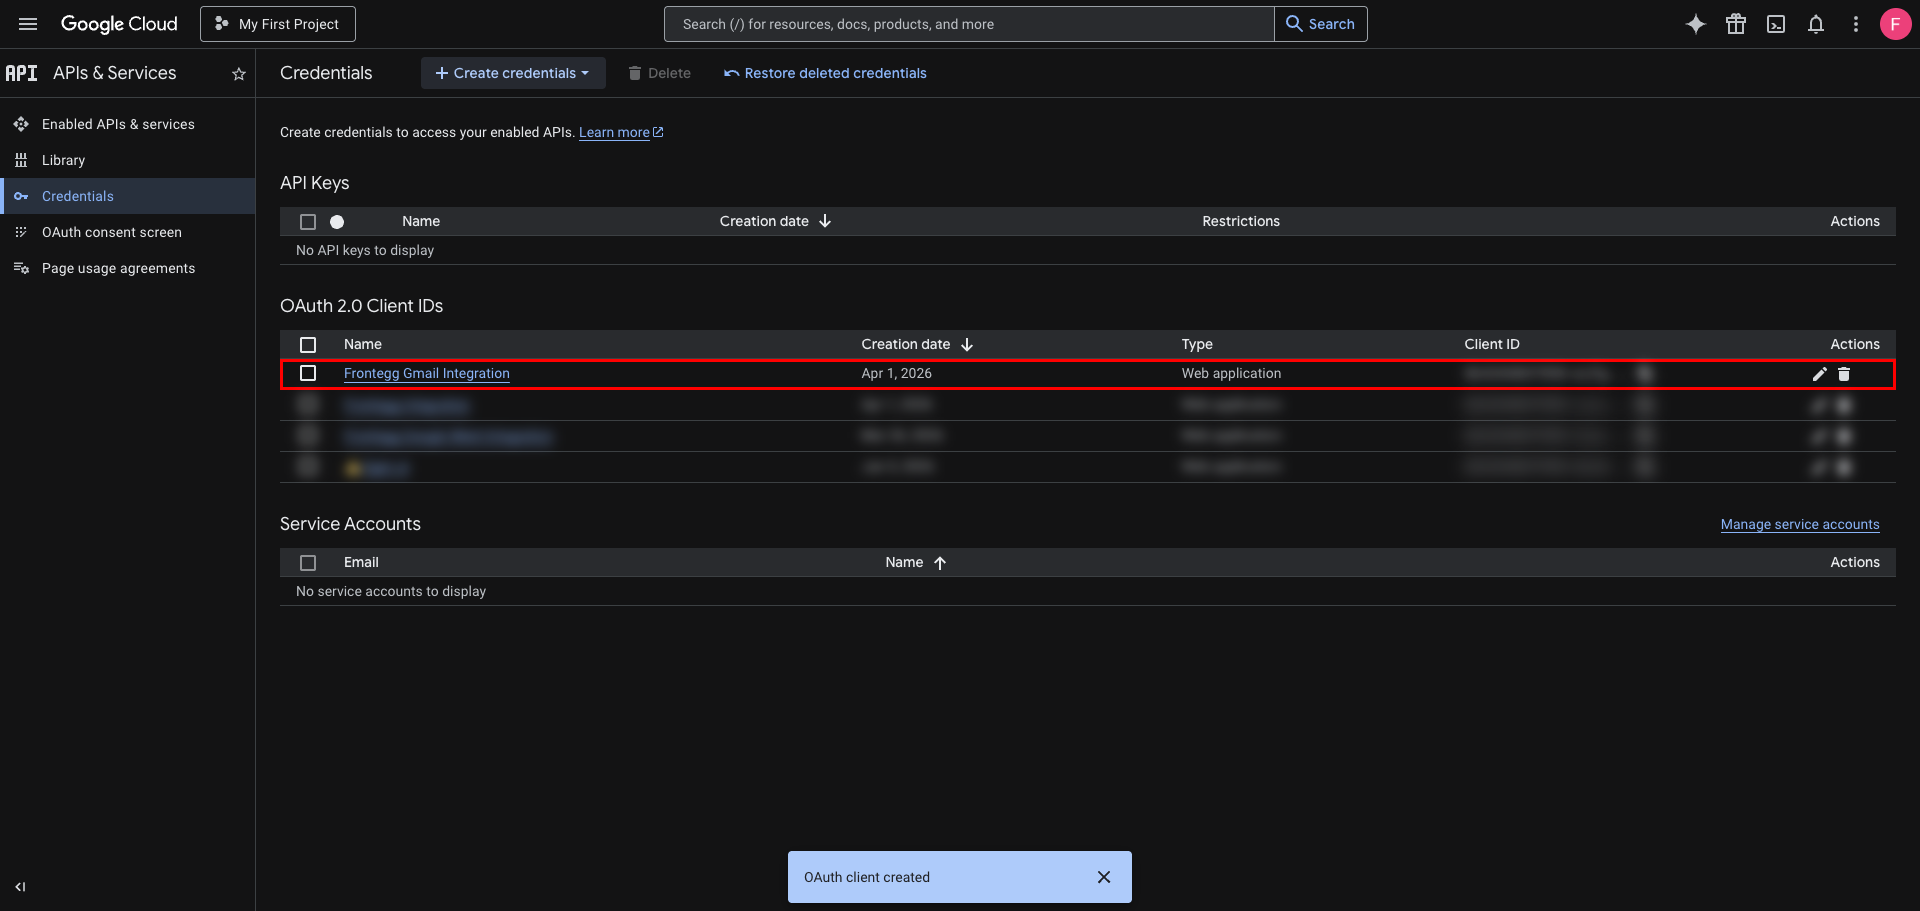
After closing the dialog, your new client appears in the OAuth 2.0 Client IDs list on the Credentials page.
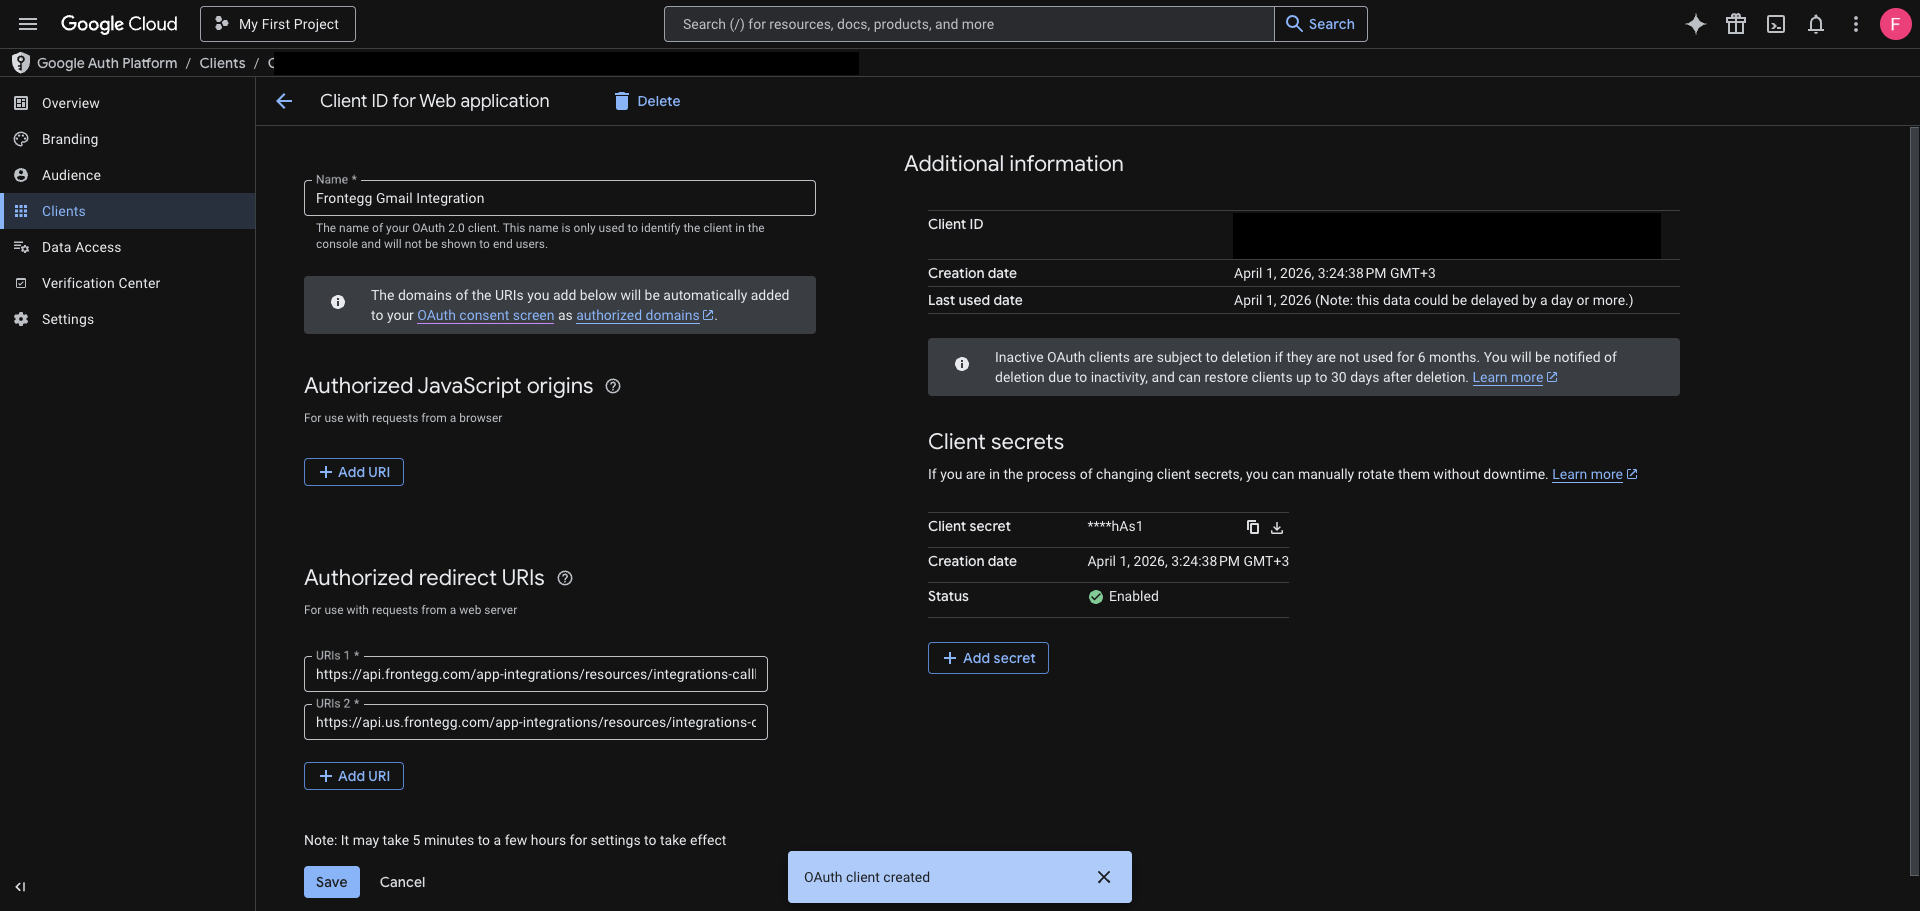
Click the client name to open its detail page. You can view and copy the Client ID at any time from the Additional information section.
Once you have your Client ID and Client Secret, enter them in the Frontegg portal:
- Open the Frontegg portal and navigate to [ENVIRONMENT] → Integrations → Gmail.
- Enter the Client ID and Client Secret in the corresponding fields.
- Select the required scopes:
| Scope | Description |
|---|---|
https://www.googleapis.com/auth/gmail.readonly | List and read messages, threads, labels, drafts, and attachments |
https://www.googleapis.com/auth/gmail.modify | Modify, trash, and untrash messages and threads, including in bulk |
https://www.googleapis.com/auth/gmail.compose | Create, update, delete, and send drafts |
https://www.googleapis.com/auth/gmail.send | Send a message directly, without creating a draft first |
https://www.googleapis.com/auth/gmail.labels | Create, update, and delete labels |
https://mail.google.com/ | Permanently delete messages and threads, including in bulk |
- Click Save.
Keep your credentials secure
Keep your credentials secure
Never share or commit your Client Secret to version control.